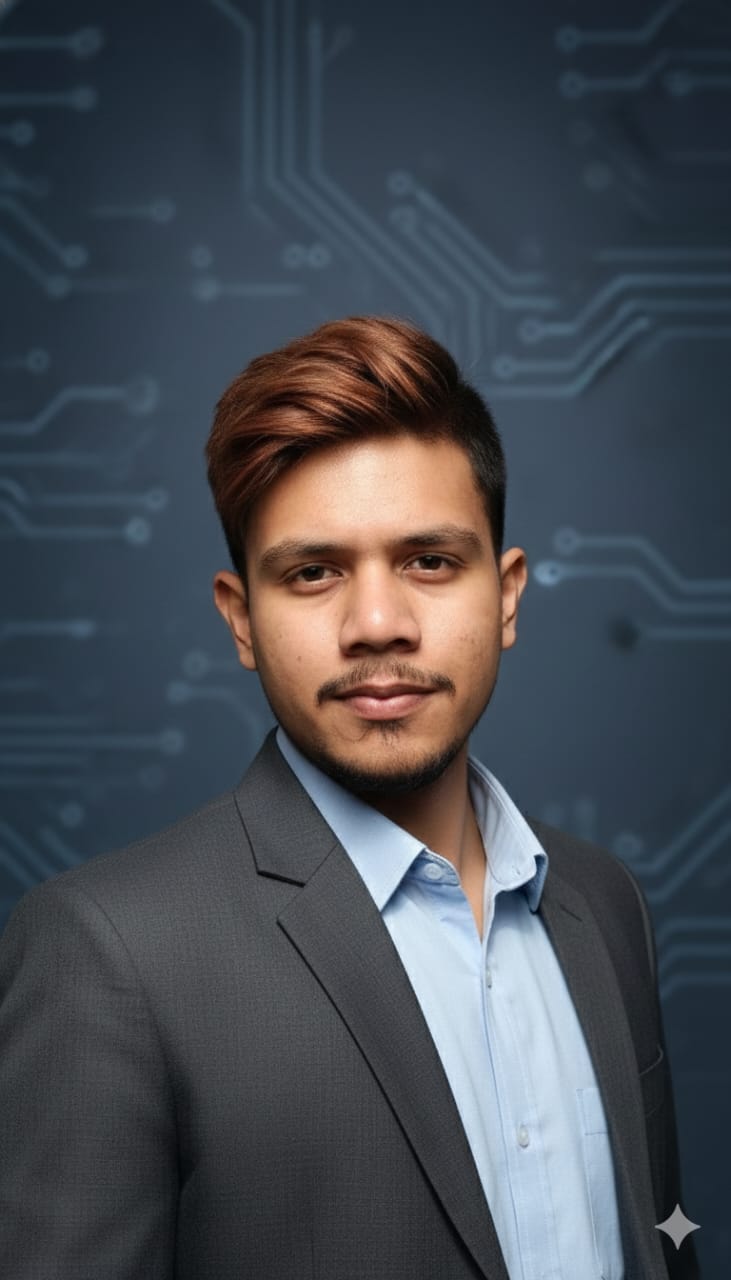
Abhirup Sarkar
Security specialist turning offensive knowledge into defensive strength. I break systems ethically — exposing vulnerabilities before malicious actors can exploit them.
My Skills
Tools Arsenal
Battle-tested tools that power every engagement — from recon to post-exploitation.
Web App Testing
- Burp Suite — Intercept, analyze & exploit HTTP traffic
- OWASP ZAP — Open-source web vulnerability scanner
- Nuclei — Template-based fast vuln scanning
- FFUF / Gobuster — Directory & subdomain fuzzing
- Nessus / OpenVas — Vulnerability Scanning & Assessment
Enumeration & Recon
- Nmap — Network mapping, port & service detection
- Amass — Full attack surface mapping
- Subfinder — Passive subdomain enumeration
- Dirsearch — High-speed directory brute-forcing
- Netcat — The Swiss army knife of networking
- Nikto — Web Vuln Recon
Cracking & Analysis
- Hashcat — GPU-accelerated password cracking
- John the Ripper — Local hash & password attacks
- Wireshark — Deep packet capture & analysis
- TCPDump — CLI packet capture & filtering
Exploitation
- Metasploit — Exploitation & post-exploitation framework
- SQLmap — Automated SQL injection & takeover
- Hydra — High-speed credential brute-force
- Custom XSS/CSRF — Browser exploitation tooling
Privilege Escalation
- LinPEAS / WinPEAS — Automated priv-esc enumeration
- SUID / Capabilities — Binary abuse techniques
- PATH Hijacking — Service & cron exploitation
- Credential Discovery — SSH keys, config secrets
Red Team Ops
- Impacket — AD auth, command execution toolkit
- Evil-WinRM — Stable shell on compromised Windows
- CrackMapExec — Cred testing & lateral movement
- smbclient / enum4linux — SMB enumeration & exploitation
Certifications
Verified credentials validating real-world offensive security competency.
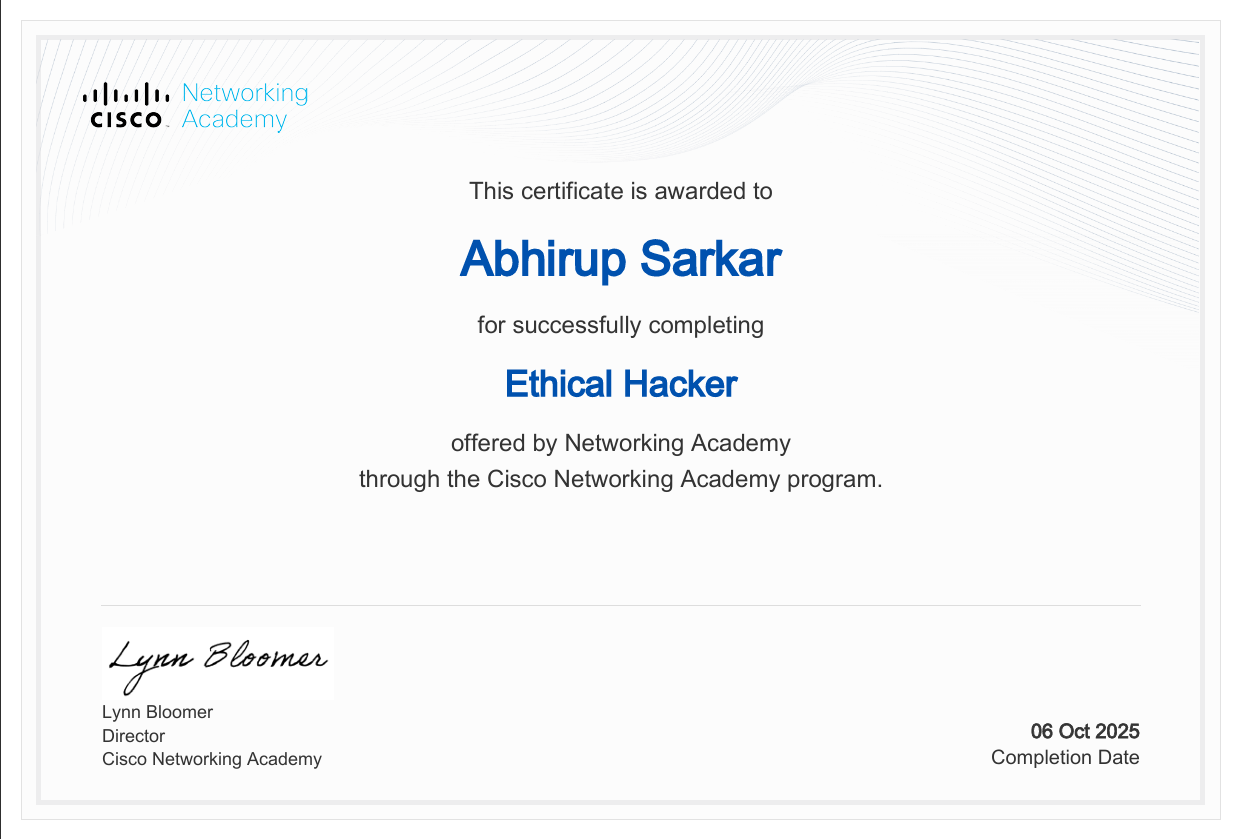
Web hacking, network exploitation, Metasploit, privilege escalation, and Active Directory attack paths.
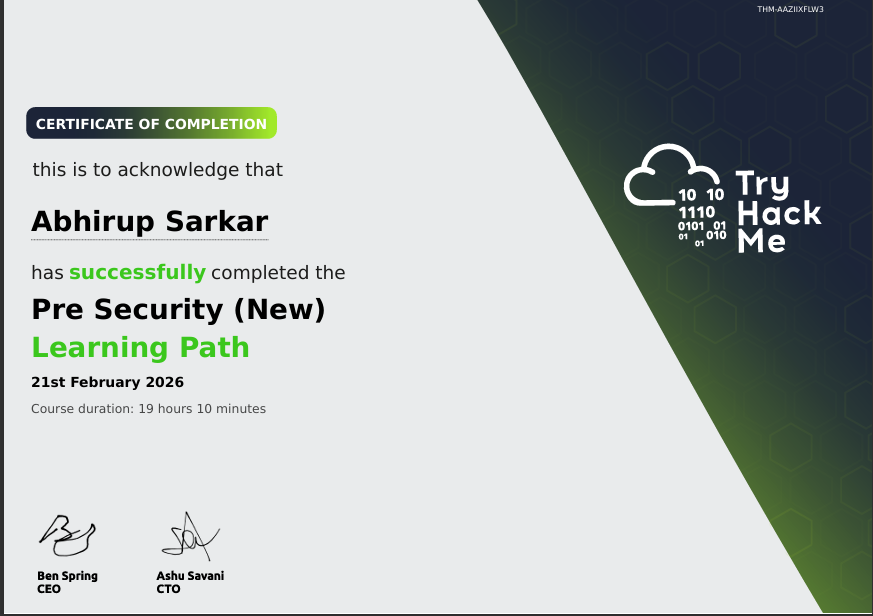
Discover how networking, the web, and real world cyber attacks all connect.
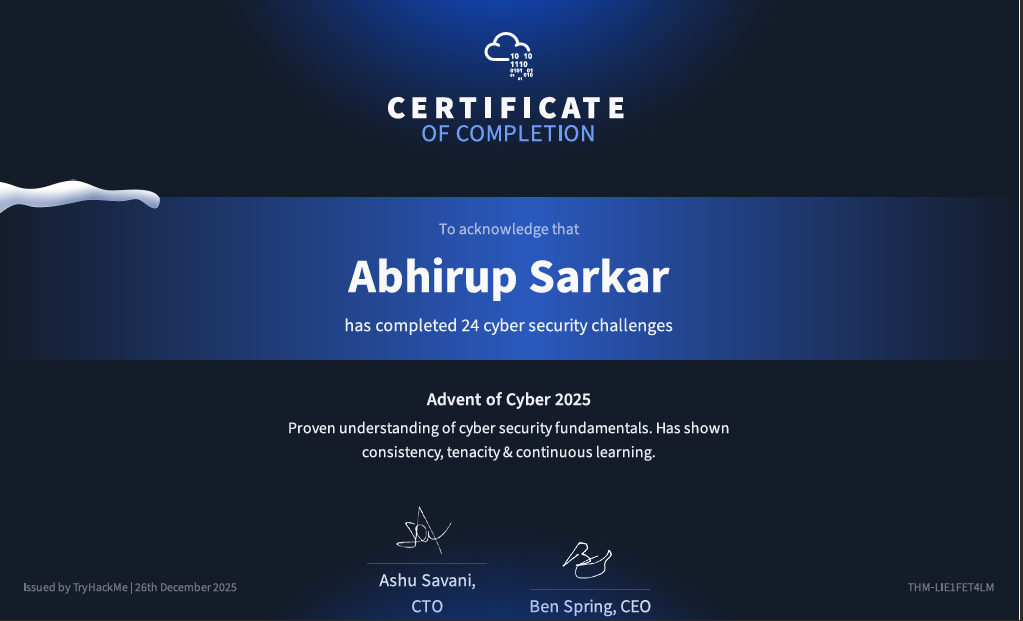
Completed 24 cyber security challenges covering a wide range of offensive and defensive techniques.
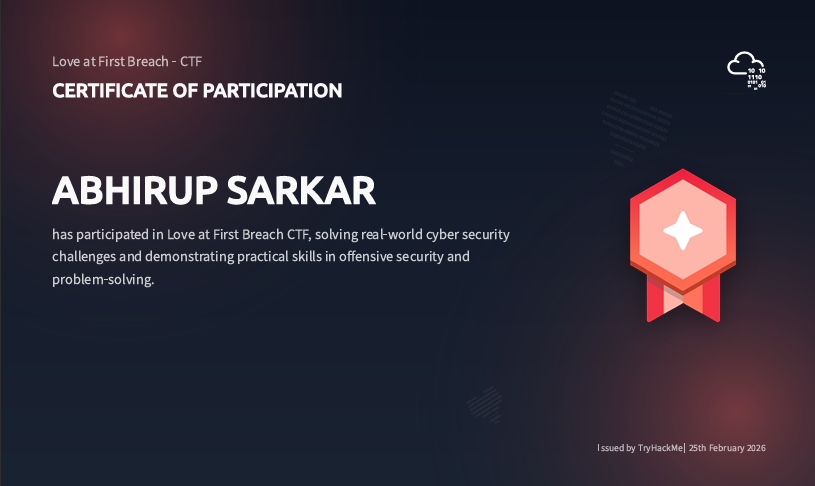
Capture The Flag event focusing on offensive security techniques and exploit development.
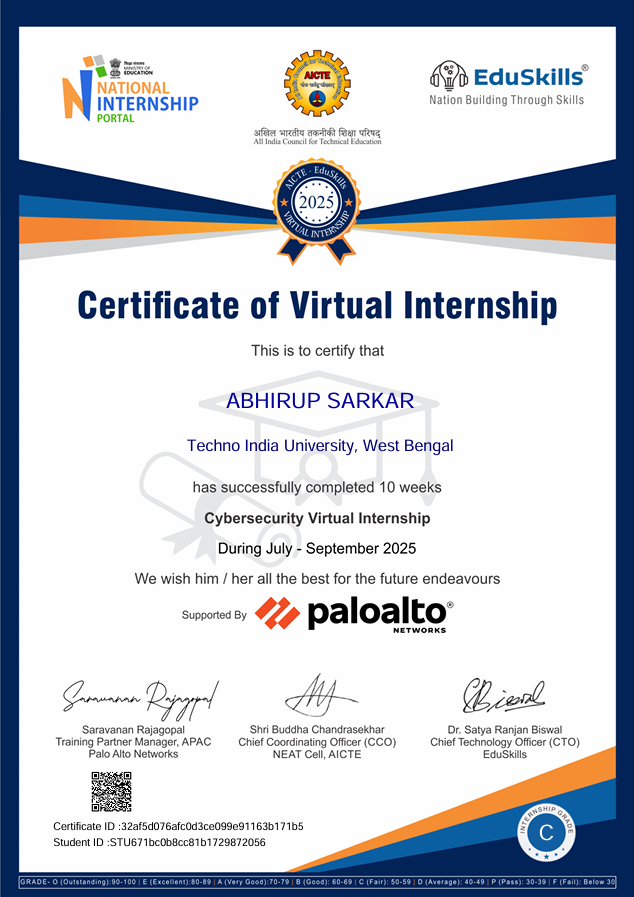
Foundational security concepts, threat landscape awareness, and best practices for organizational defense.
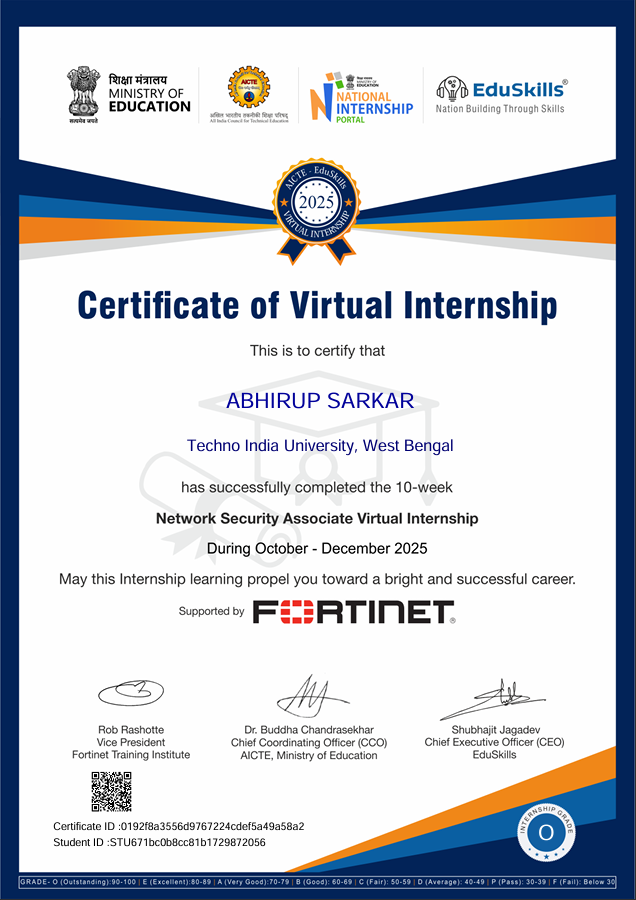
Covers network security fundamentals, ethical hacking, and incident response using FortiGate solutions.
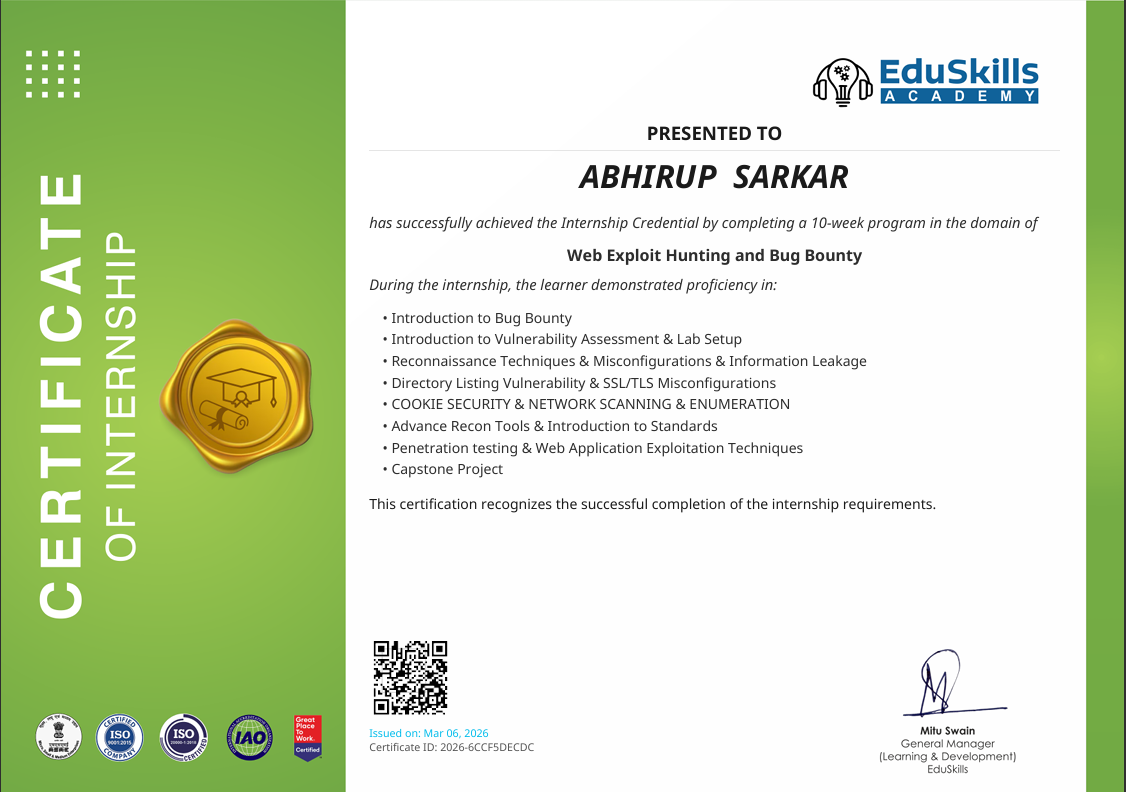
Trains students in identifying and mitigating real-world web application vulnerabilities.
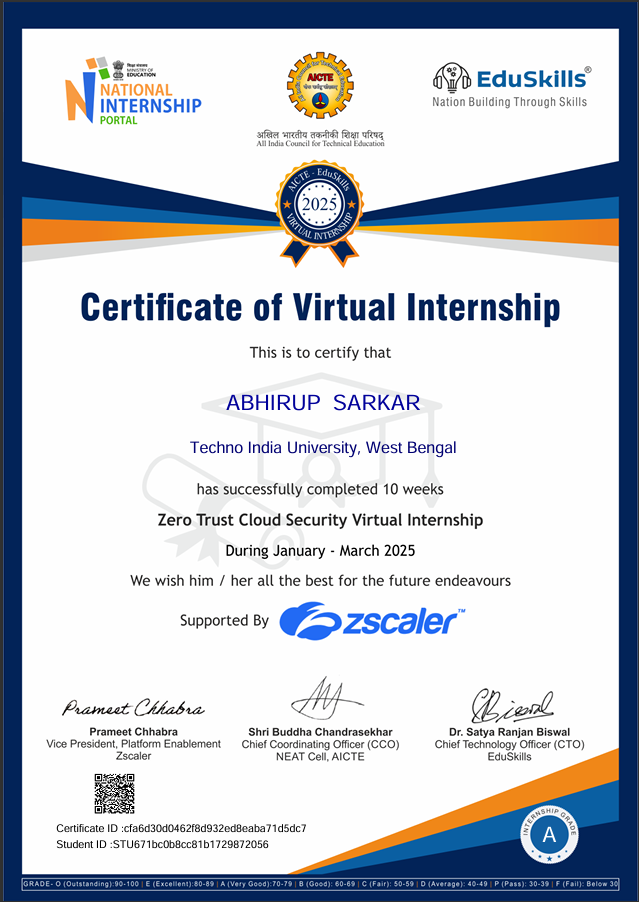
Hands-on experience in ZIA and ZPA to secure cloud-first environments using Zero Trust principles.
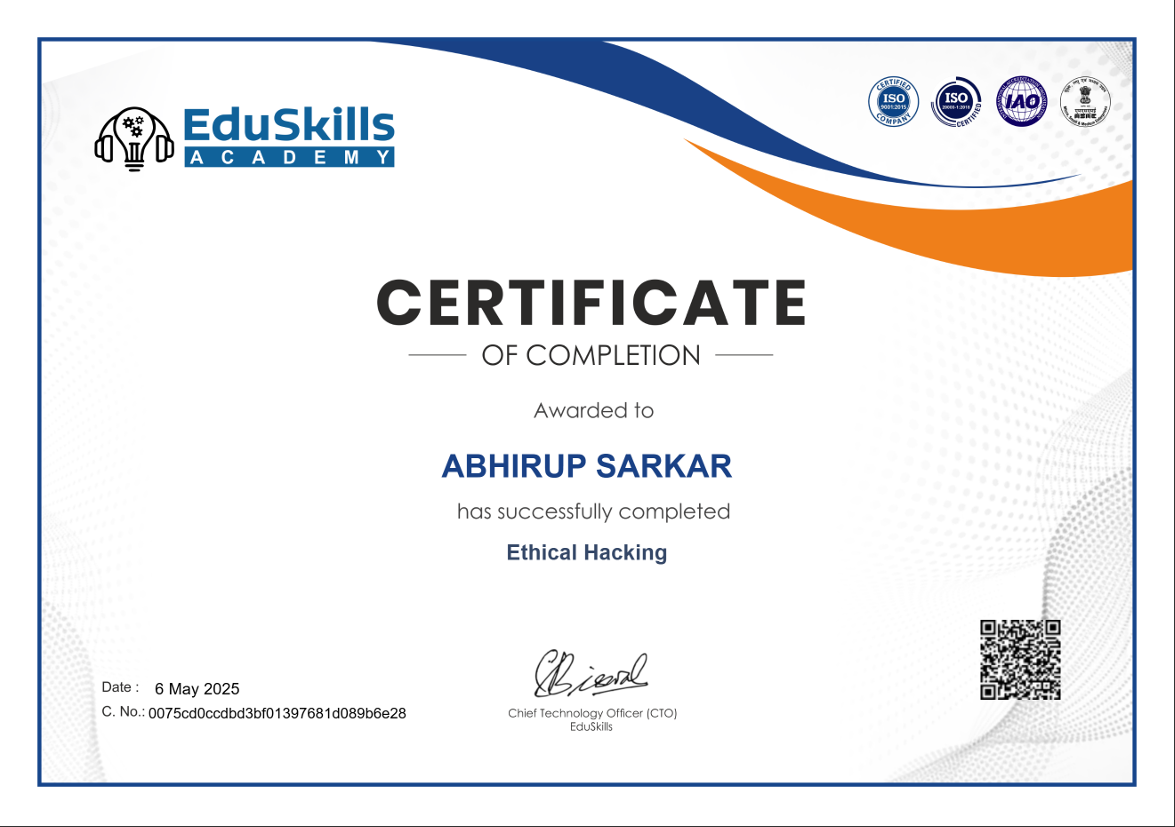
Covers footprinting, scanning networks, enumeration, and system hacking methodologies.
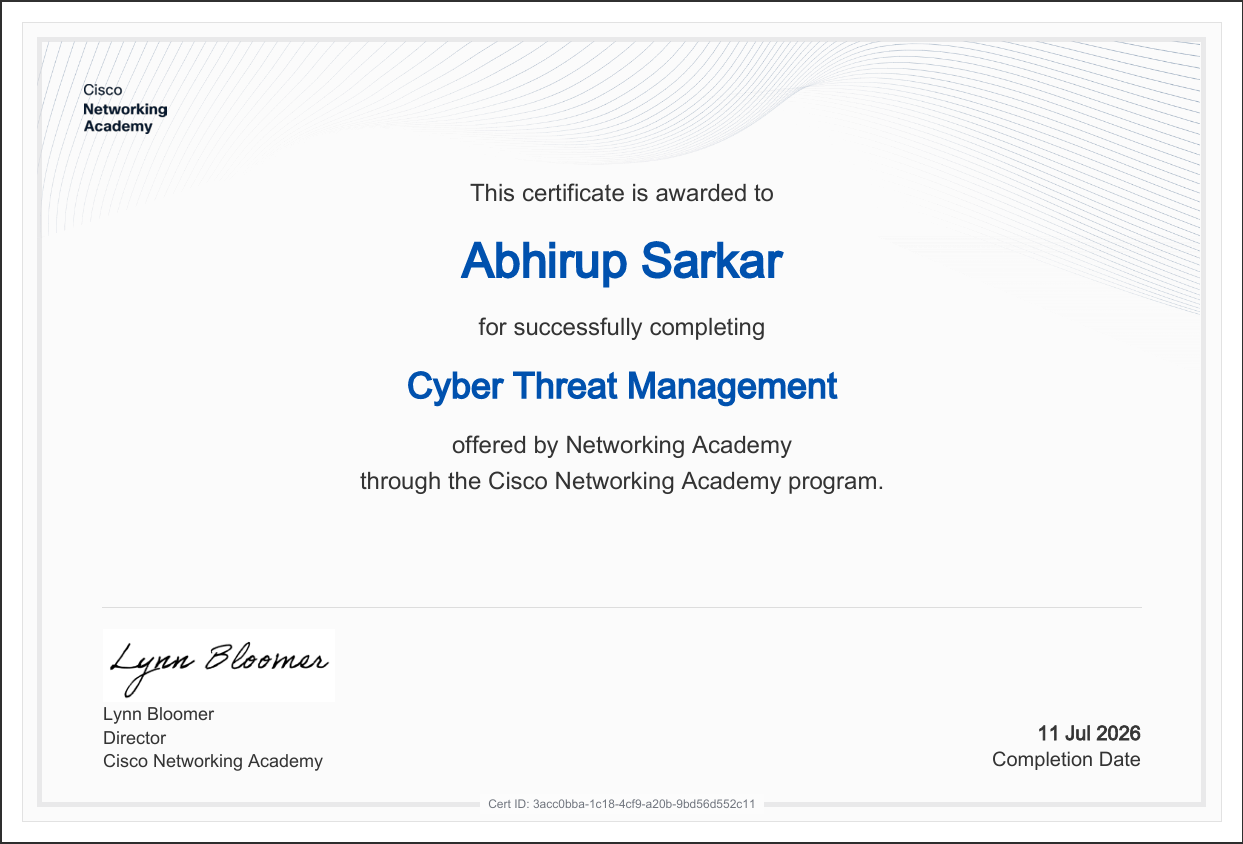
Covers incident response, scanning networks, enumeration, SIEM/SOAR and system forensics.
CVE Highlight
CVE-2026-77177
Security vulnerability publicly documented in the Common Vulnerabilities and Exposures (CVE) system. View the official record and NVD entry for verification.
Journey Timeline
Key milestones in my cybersecurity career and learning path.
Independent Security Researcher
Active bug hunter on HackerOne, BugCrowd, YesWeHack, Com Olho and responsible disclosure programs. Found 50+ vulnerabilities ranging from authentication bypasses to critical account takeovers. Focus on web application security and API exploitation.
Advanced Certifications
Completed advanced training in Penetration Testing, Red Team Operations, and Vulnerability Assessment methodologies. Achieved 10+ industry-recognized certifications.
CTF & Bug Bounty Success
Competed in multiple Capture The Flag competitions and TryHackMe challenges. Developed custom exploitation tools and security automation scripts. Built reputation as skilled Pentester in the security community.
Full-Stack Security Learning
Mastered penetration testing frameworks (Metasploit, Burp Suite), reconnaissance tools (Nmap, Amass), and exploitation techniques. Developed expertise in OWASP Top 10 vulnerabilities and secure code review.
Security Foundations
Started cybersecurity journey learning Linux, networking fundamentals, and basic penetration testing. Built home lab and started contributing to open-source security projects.
My Projects
 Web
NETVY Web Service
Platform providing SEO optimization, web development, and malware analysis services.
 Security
CyberXploit Pro
Comprehensive penetration testing toolkit designed for ethical hackers and red teamers.
 AI
J.A.R.V.I.S.
AI-powered security analysis assistant for threat detection and automated reporting.
 Toolkit
Phantom X
Custom multi-wrapper offensive toolkit built for VAPT analysts and red team ops.
 CLI
AURA
Lightweight web security scanner CLI for fast reconnaissance and vulnerability auditing.
 Room
Methodical Mindset – Intermediate Penetration
This room develops structured reasoning for professional penetration testing. Rather than focusing on isolated exploits, you will learn how to analyze systems holistically, apply structured workflows, evaluate exposure, and communicate findings responsibly.
 CLI
JSPECTER
JSPECTER - Autonomous JS Recon & Vulnerability Intelligence Engine
 Web
PayloadVault
Hackers-Encyclopedia with numerous Payloads and techniques.
 Web
Prem-Bhakti
In the love of Radha Krishna, the devotion of Ram Sita, and the union of Shiv Shakti, lies eternal Prem Bhakti 🕉️✨
My Blog
Deep-dive writeups on pentesting, red teaming, CTF challenges, and AI in security.
Medium — @0xAbhiSec
In-depth security research, CTF walkthroughs, real-world pentest techniques, and vulnerability analysis. Covering everything from OWASP exploits to AI-powered threat detection.
About Me
I'm Abhirup Sarkar — a dedicated Ethical Hacker and Penetration Tester with a deep passion for uncovering vulnerabilities and turning them into hardened defenses.
With 2+ years in the field, I've conducted security assessments across web applications, APIs, and enterprise networks — simulating real-world adversary tactics to expose blind spots before malicious actors find them.
My focus areas: offensive security, vulnerability research, red team operations, and integrating AI/ML into security workflows for smarter, faster threat detection and response.
When not inside a CTF or lab environment, I write technical blogs on Medium, contribute to open-source security tools, and chase the next OSCP milestone.
Hire Me
Available for freelance pentesting engagements, vulnerability assessments, and full-time security roles.
Download Resume
Full experience, education, projects, and certifications in one document.
Hello, operator. I'm Abhirup's security assistant. Ask me about his skills, projects, bug findings, or how to hire him.